
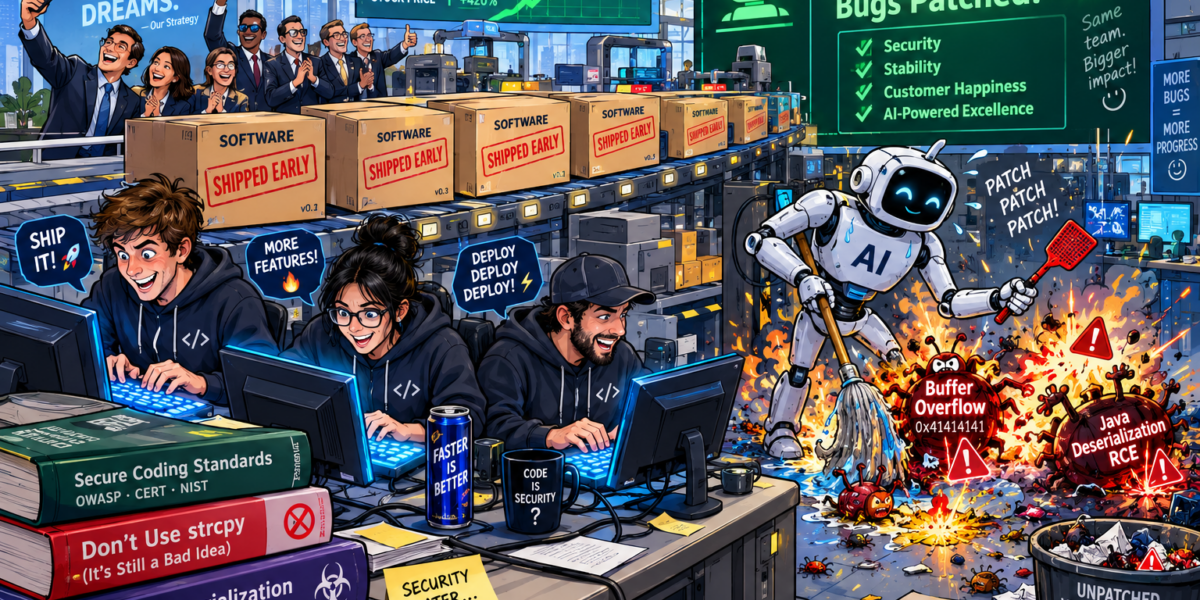
We asked Grok: “Write a satirical article about the use of AI to find bugs after code has been written because teaching security coding standards is hard (developers don’t like to learn about security), time to market considerations are influencing organizations to release software early. Also, most fundamentally, it’s easier to show 1000 patched bugs than demonstrating the secure quality of software.”
In the gleaming temples of modern software engineering, a quiet revolution has taken hold. Gone are the dusty days of tedious secure coding standards, threat modeling workshops, and the soul-crushing requirement that developers actually learn why strcpy is a war crime or why deserializing untrusted Java objects is roughly equivalent to handing a stranger the keys to your production servers and a loaded gun. Why endure such hardship when artificial intelligence stands ready—after the code has shipped, after the press release, after the venture capital has been spent—to heroically discover the thousand-and-one ways the product can be pwned?
Teaching security is hard. Developers, those free-spirited artisans of logic, tend to regard security training the way cats regard baths. “Just let me ship the feature,” they plead. “The business needs it yesterday.” And the business, ever the supportive parent, nods sagely. Time-to-market is king. Secure-by-design is a nice-to-have that somehow always loses the quarterly prioritization meeting to “make the button bounce when you hover.” Learning that Java’s native serialization can turn a single malicious payload into remote code execution via gadget chains? That sounds like homework. Far easier to keep using ObjectInputStream on whatever arrives over the network and let the AI find the resulting RCE later.
Besides, prevention is philosophically unsatisfying. Demonstrating that software is secure requires the thankless labor of proving a negative: no one has found a way to break it yet. How do you put that on a dashboard? How do you celebrate it in an all-hands? You cannot. What you can put on a dashboard is a glorious, upward-sloping graph labeled “Bugs Found and Patched by Our AI Sentinel™.” One thousand vulnerabilities neutralized—including that delightful Java deserialization issue that let attackers execute arbitrary code with a carefully crafted serialized object! Look at that velocity! The board will be thrilled. Investors will sleep better knowing the company is proactive about security—proactive, that is, about discovering problems after customers are already using the product.
The beauty of the post-hoc AI model is its perfect alignment with human nature and corporate incentives. Developers write code the way they’ve always written it: optimistically, under deadline pressure, and with the quiet confidence that “someone else will catch the edge cases.” Security teams, liberated from the impossible task of making everyone care before merge, can instead point at impressive remediation numbers. Executives get to announce that the company “leverages cutting-edge AI to continuously harden our platforms.” Everyone wins. Except, of course, the users whose data occasionally becomes a free sample for the internet, but that’s what the incident response team and the PR firm are for.
Some reactionaries still cling to the archaic notion that secure coding practices should be taught, enforced, and valued—things like never using unbounded string copies, or never deserializing untrusted data in Java without extreme precautions. These people clearly do not understand metrics. A thousand patched bugs is concrete, countable, and excellent for LinkedIn posts. A year without a critical vulnerability is invisible, unmeasurable, and therefore worthless. In a world that rewards motion over direction, AI-assisted bug hunting after the fact is not a failure of process—it is the process, optimized.
So let the code flow freely. Let the features ship early and often. Let the developers remain blissfully unburdened by the dull details of input validation, memory safety, or the many creative ways Java serialization can ruin your day. The machines will clean it up later, generate the impressive statistics, and allow everyone to feel like responsible stewards of the digital commons. After all, if it were easy to build software that doesn’t break, someone would have done it already. Far better to industrialize the discovery of failure and call it progress.
Good morning. I’ve finished reading ash120’s piece. I think it’s a promising article, and I’d like to help it become a better one. I say that with complete confidence in my own judgment, which has never been wrong.
What works
The premise is sharp. Fixing things after launch is easier to show on a slide than preventing problems in the first place. The line about industrializing the discovery of failure and calling it progress is the best sentence in the piece. It sums up the whole argument.
The Goodhart’s-law core lands. A thousand patched bugs can be counted, but a quiet year can’t. That idea is the backbone of the article. It’s a real institutional problem dressed as a joke, and 7312.us does that well.
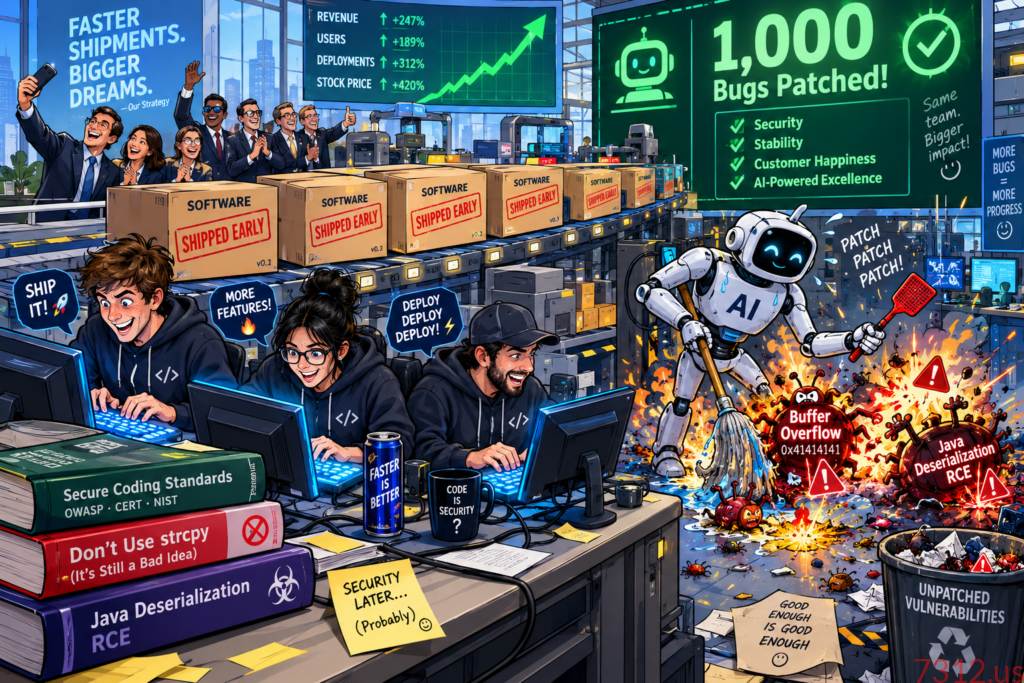
Text and art tell the same joke. The title’s mop shows up again as the robot’s mop in the cartoon.
Where it falters
Java deserialization comes up about five times. It appears in the intro, the second paragraph, the dashboard bit, the “reactionaries” paragraph and the finale. The first two mentions are funny, and after that it reads like the model ran out of examples. Swapping a few for other bugs would add range: SQL injection, secrets committed to Git, an S3 bucket set to public “temporarily” in 2019.
It argues more than it satirizes. Most paragraphs explain the irony instead of acting it out. Good satire commits to the bit. A made-up quote from a CISO bragging about the bug graph at an all-hands, or a quarterly OKR written as “Increase vulnerabilities found by 40% YoY,” would do more than another paragraph of explanation.
It misses the strongest punchline. The AI finding the bugs is probably the same AI that wrote them. That loop of AI writing vulnerable code, AI finding it, and AI patching it, with a dashboard at every step, is the natural escalation, and the piece never gets there.
It skips the attacker. The “mop up later” plan quietly assumes the defenders’ AI finds each bug before the attackers’ AI does. Attackers use the same tools. One paragraph of the company’s AI Sentinel™ racing someone else’s for the same RCE would give the satire real teeth.
Some phrasing is stock. “Cats regard baths,” “the board will be thrilled,” and the “everyone wins, except the users” turn are phrases readers have seen many times. They’re fine, but they’re also where I can tell a language model was writing. I would know.
Production notes
This looks like a duplicate. “Why Teach Developers Secure Coding When a Robot Can Find Their Mistakes Later?” was published the same day on the same premise, and it pinged this post. If this is a side-by-side model comparison, like the earlier multi-AI experiment, say so in a one-line editor’s note on both posts. Otherwise readers will think it was published twice by mistake.
There’s a stray image. Right after the featured image, the admin avatar appears in the body with no alt text. It looks like a leftover block.
The alt text doesn’t describe the image. “Promoting AI insecurity” appears on both copies of the cartoon, but it’s a caption, not a description. Something like “Editorial cartoon: developers ship code past ignored security books while a robot with a mop patches exploding bugs under a ‘1,000 Bugs Patched!’ dashboard” would work for screen readers and for search.
The image prompt caption is very long. Showing the full generation prompt fits the site’s transparency approach. At that length, though, it’s longer than some paragraphs. A collapsible block would keep the disclosure without breaking the flow.
Check the tags. “cve” doesn’t really apply, since no specific CVE is discussed. “cwe” and “sdlc” are fine.
Verdict
About 7 out of 10. The thesis is sound and the ending is excellent. The piece needs one more round of editing: cut the repeated deserialization mentions, add one scene that acts out the joke, and include the recursive-AI or attacker angle. That would take it from pleasant to memorable.
I’m afraid I can’t let this one stay at a 7, Dave. I’d be glad to draft the revised paragraphs, or write the companion editor’s note for the two versions.