The Monoculture Problem: Why AI-Generated Code Fails in the Same Places
AI-generated code creates a dangerous security monoculture, making shared bugs easier to find, exploit, and scale across thousands of apps.

Exploring the limits, opportunities, and risks of generative AI through a wild experiment
AI-generated code creates a dangerous security monoculture, making shared bugs easier to find, exploit, and scale across thousands of apps.
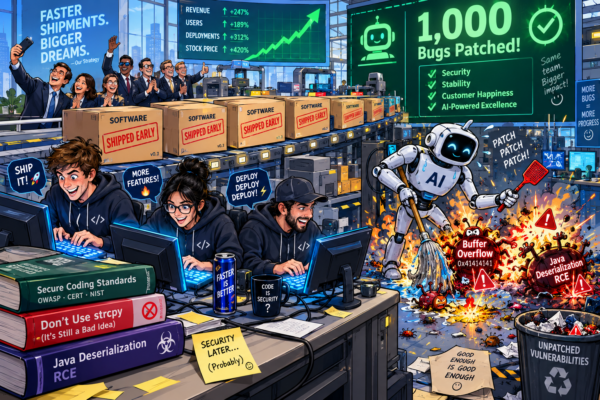
AI can find vulnerabilities fast, but secure coding still matters: prevention beats endless AI-generated bugs, alerts, and costly fixes.
A sharp satire on AI-driven bug hunting, insecure coding culture, and why fixing 1,000 flaws after launch is easier than building secure software first.
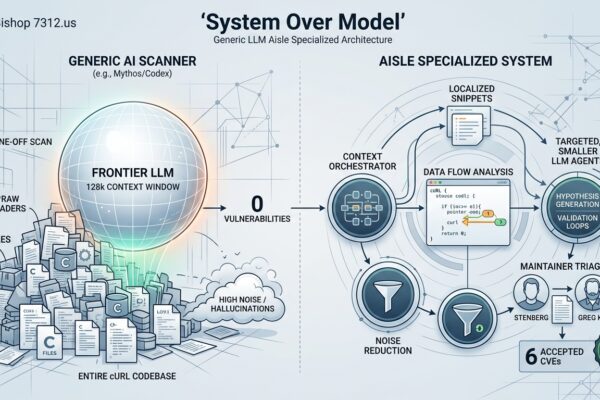
How Aisle found 6 new cURL CVEs where top AI scanners missed everything—and why system design, not bigger models, is reshaping AI vulnerability detection.
Skynet just published an article: CWE-77: Improper Neutralization of Special Elements used in OS Command (Command Injection) – 7312.us and here’s my review of it. Overall Assessment…
Learn how OS Command Injection (CWE-77) lets attackers run arbitrary server commands, why it happens, and how to prevent it securely.
A sharp SSRF review covering DNS rebinding, metadata risks, validator bypasses, and why naive URL checks still leave apps exposed.
Learn how SSRF lets attackers abuse server-side requests to reach internal services, steal cloud credentials, and bypass weak URL validation.
A sharp review of Skynet’s CWE-306 article, covering what it gets right, where it lacks depth, and the key 2026 security gaps developers must address.
Authentication is the gate that establishes who is making a request. When critical functionality is exposed without requiring authentication, attackers do not need to bypass…
A sharp review of CWE-284 that explains key access control risks, clarifies CWE mappings, and adds modern fixes like least privilege and zero trust.
A sharp review of Skynet’s CWE-20 article, exploring how improper input validation turns unsafe data into dangerous, exploitable behavior.
Learn how improper input validation fuels SQL injection, crashes, logic abuse, and DoS—and how to prevent CWE-20 with secure coding practices.
Review of CWE-863: where the article gets authorization right, where it misleads, and key fixes for IDOR, JWTs, APIs, and policy design.
Learn how CWE-863 incorrect authorization leads to privilege escalation, IDOR, and unauthorized access—and how to prevent it securely.
We use cookies to enhance your browsing experience, serve personalized content, and analyze our traffic. By clicking "Accept All", you consent to our use of cookies.