Practical recommendations for employers, cybersecurity teams, recruiters, and individuals
Introduction
Remote work has expanded access to global talent, but it has also created opportunities for sophisticated employment fraud. A public service announcement issued by the FBI’s Internet Crime Complaint Center (IC3) on October 13, 2026, warns that North Korean information technology (IT) workers are expanding their use of intermediaries, stolen identities, and subcontractors to infiltrate Western companies. These schemes can generate revenue for the North Korean government while exposing employers to intellectual property theft, data breaches, extortion, and legal consequences.
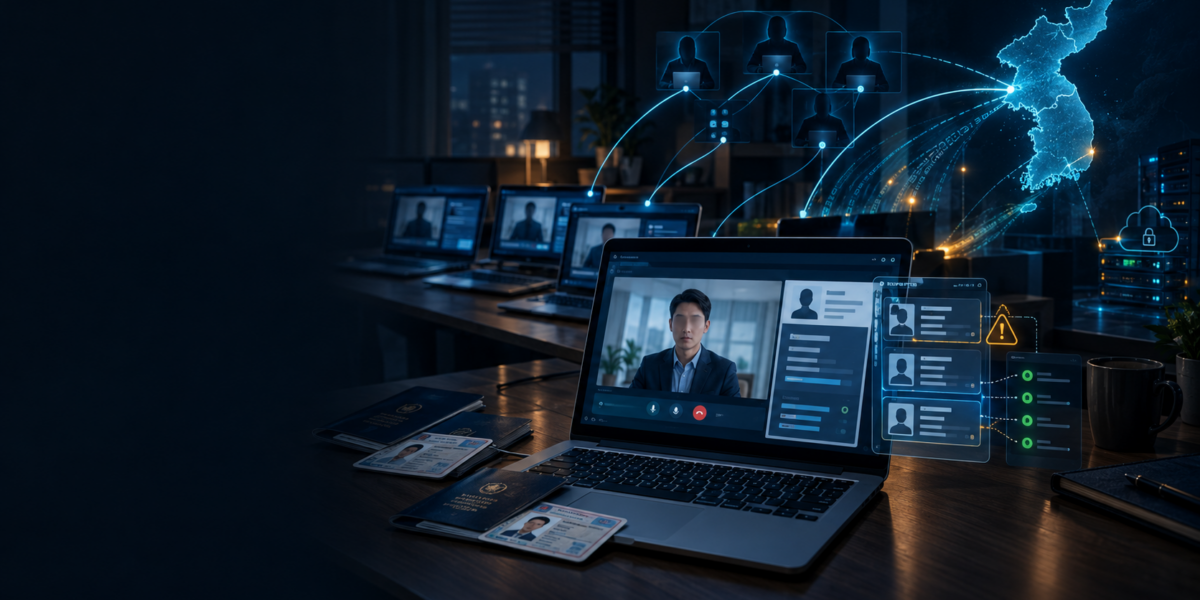
The warning, titled “North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment,” highlights an important change in the threat: fraudulent applicants are no longer relying solely on fake résumés or deceptive online interviews. They may recruit people inside the United States to participate in hiring interviews, host company-issued laptops, provide legitimate online identities, or facilitate access to corporate systems. Some intermediaries may understand the scheme; others may be misled about the nature of the work.
Artificial intelligence (AI) adds another dimension. It can help organizations detect suspicious activity, but it can also help attackers create convincing professional identities, prepare for interviews, and evade traditional verification procedures. Effective defense therefore requires more than detecting deepfakes or checking identity documents. It requires layered verification throughout the employment lifecycle.
Source: FBI IC3, Public Service Announcement, October 13, 2026.
1. Understanding the threat
The FBI describes a scheme in which North Korean IT workers obtain remote employment under false or stolen identities, collect salaries, and potentially exploit their access to company systems. The latest advisory emphasizes the growing role of facilitators and third-party labor.
The scheme can involve several interconnected activities:
- Identity fraud: Applicants use stolen personal information, fabricated documents, or professional profiles belonging to other people.
- Interview impersonation: A facilitator or hired third party participates in an interview or meeting in place of the person who will actually perform the job.
- Laptop farms: U.S.-based intermediaries host employer-issued computers at their homes, allowing overseas operators to make their activity appear to originate domestically.
- Unauthorized remote access: Workers use remote desktop software, remote management tools, or external keyboard-video-mouse devices to control employer-provided computers from elsewhere.
- Undisclosed subcontracting: A person hired by a company transfers some or all of the work to other individuals, obscuring who actually has access to company information.
- Data theft and extortion: Insiders may copy proprietary data or threaten to disclose sensitive information to demand additional payments.
The latest advisory also reports cases involving threats of physical violence and intimidation to compel facilitators or former employers to cooperate or pay money. These incidents demonstrate that the consequences can extend beyond ordinary employment fraud.
A central lesson is that a legitimate-looking employee account does not necessarily establish the identity, location, or trustworthiness of the person operating it. A candidate may pass one check while the overall arrangement remains fraudulent.
Source: FBI IC3, October 13, 2026 advisory.
2. Specific recommendations for individuals
People seeking additional income through remote work, freelance contracts, or temporary assignments should be particularly cautious about offers that appear simple, flexible, and unusually well paid.
A. Never rent out your identity or professional accounts
Do not allow another person to use your:
- Government-issued identification or identity-verification documents.
- Social media or professional networking accounts.
- Job-search accounts, email addresses, or account credentials.
- Bank accounts or payment services.
- Face, voice, or likeness to complete an interview or verification procedure.
A request to use your identity in exchange for money is not a harmless administrative favor. It may enable employment fraud, expose your personal information to misuse, and create legal or financial complications for you.
B. Treat laptop-hosting jobs as a major warning sign
Be skeptical of anyone offering payment to receive a company laptop, connect it to your home internet, leave it powered on, install remote-access software, or forward equipment to another person.
A legitimate employer may ship equipment to a remote employee, but you should be the actual employee, and the arrangement should be transparent and authorized. Do not host equipment for an unknown person or allow a stranger to remotely control a computer associated with a job you did not obtain yourself.
C. Verify employers independently
Before accepting a remote job:
- Find the company’s official website independently rather than relying only on a recruiter-provided link.
- Confirm the recruiter’s identity using contact information obtained from the company’s official website.
- Check that the job description, compensation, interview process, and employment contract are consistent with the company’s normal practices.
- Be wary of requests for upfront payments, cryptocurrency transfers, identity documents sent through informal channels, or access to personal accounts.
- Contact the company through an independently verified channel if any part of the arrangement seems unusual.
Professional-looking websites, convincing documentation, and polished interviews are not conclusive proof of legitimacy.
D. Protect yourself if you have already become involved
If you have provided identity documents, hosted a laptop, shared credentials, or participated in a questionable hiring process, stop any unauthorized activity and preserve relevant communications, payment records, shipping information, and account details.
Secure affected accounts, contact your bank or payment provider if financial information is involved, and report suspected activity to the FBI’s Internet Crime Complaint Center at ic3.gov. If someone threatens your life or physical safety, contact emergency services.
Do not confront suspected perpetrators yourself or destroy evidence. Seek appropriate legal or law-enforcement assistance when necessary.
Source: FBI IC3 advisory.
3. Specific recommendations for employers
The most important organizational recommendation is to adopt what the FBI calls “identity in depth”: multiple independent checks across recruitment, onboarding, employment, and offboarding.
No single indicator reliably identifies a fraudulent worker. A suspicious remote-access application, an inconsistent address, or an unusual interview is a reason to investigate in context—not automatic proof of wrongdoing.
A. Strengthen identity verification during recruitment
Employers should:
- Verify identity documents through appropriate, lawful, and trusted verification processes.
- Conduct live identity checks and compare the individual who interviews with the person who subsequently performs the work.
- Independently confirm employment history, professional qualifications, and educational credentials with the relevant organizations.
- Use additional verification for sensitive roles, privileged access, and positions involving valuable intellectual property.
- Reverify identity when there are material inconsistencies, changes to key account details, or indications that someone else may be operating the employee’s account.
For higher-risk positions, consider an in-person verification step when practical and proportionate. Where remote verification is necessary, combine live checks with independent corroboration rather than relying on a single video call.
AI-based identity and deepfake-detection tools may supplement these checks, but their results should not be treated as definitive.
B. Control the delivery and setup of company equipment
Establish a documented process for assigning, shipping, activating, and recovering corporate devices.
- Ship equipment only to a verified address associated with the employee, subject to applicable privacy and employment requirements.
- Require additional verification for address changes or requests to redirect a laptop.
- Maintain an inventory of devices, assigned users, serial numbers, and approved configurations.
- Enroll computers in endpoint management before granting access to sensitive systems.
- Disable unauthorized remote-control tools and restrict software installation through centrally managed policies.
- Investigate repeated remote connections, unexpected peripheral devices, or other deviations from approved configurations.
A laptop’s physical location is not proof of the operator’s location. Device management must therefore be paired with identity checks and monitoring of how the device is used.
C. Monitor for suspicious activity after hiring
Pre-employment screening alone cannot prevent a fraudulent insider from accessing systems. Security controls must remain active throughout employment.
Recommended measures include:
- Endpoint detection and response (EDR): Identify suspicious processes, unauthorized software, unusual connections, and attempts to collect or transfer data.
- Identity and access management (IAM): Apply least privilege, strong authentication, and role-based permissions.
- Network monitoring: Investigate unusual outbound traffic, unexpected remote desktop sessions, and connections inconsistent with the employee’s duties.
- Data loss prevention (DLP): Detect unauthorized transfers of source code, customer information, credentials, and confidential documents.
- Centralized logging: Correlate identity, endpoint, network, cloud, and application events to identify patterns that isolated alerts might miss.
- Periodic access reviews: Reassess whether an employee’s access remains necessary, especially after role changes or unusual account activity.
Organizations should also investigate unexplained changes to payment details, contact information, shipping addresses, or other identifiers. These signals are most useful when correlated with independent evidence.
D. Manage contractors and staffing firms as part of the same risk
A third-party staffing firm does not eliminate the employer’s responsibility to protect its systems and information.
Companies should require vendors to document identity-verification procedures, control subcontracting, disclose who will actually perform the work, and notify the client of personnel changes. Contract terms should establish security requirements, audit rights, data-handling expectations, and incident-reporting obligations.
Before granting access to a contractor, confirm the actual individual’s identity and authorize only the systems and information needed for the contracted work. Revoke access promptly when assignments end.
E. Establish a coordinated response process
Human resources, recruiting, information technology, cybersecurity, legal, compliance, and management should share relevant signals through a documented investigation process.
If a suspected fraudulent worker is identified:
- Escalate the concern to the appropriate security and legal teams.
- Preserve relevant logs, device records, communications, and access histories.
- Assess whether corporate accounts, devices, credentials, or data may be compromised.
- Restrict access proportionately while preserving evidence and avoiding unnecessary disruption to legitimate employees.
- Rotate exposed credentials, revoke unauthorized access, and investigate possible data exfiltration.
- Report suspected activity to the FBI and IC3 and follow applicable legal and regulatory requirements.
Because the FBI has documented threats against former managers and companies, incident-response plans should also address employee safety, executive protection when appropriate, and escalation to law enforcement.
The objective is not simply to reject suspicious applicants. It is to prevent unauthorized access, detect abuse early, and contain damage if screening fails.Writing
4. AI as a defensive tool: Turning the attacker’s advantage into a security capability
AI can help organizations detect suspicious behavior that would be difficult to identify through manual review alone. The most effective applications combine AI’s ability to analyze large volumes of data with independent verification, established security controls, and human judgment.
A. Detect identity inconsistencies across the hiring process
AI-assisted systems can help compare information across résumés, applications, interview records, employment histories, and onboarding documents.
For example, an organization could use an approved analysis system to flag:
- Repeated résumé language, contact information, or portfolio content across ostensibly unrelated applicants.
- Material inconsistencies between an application and independently verified employment history.
- Unusual patterns of account creation, identity changes, or repeated applications.
- Possible mismatches between the person who completed the interview and the person subsequently appearing in work-related interactions.
These findings should trigger verification, not automatic rejection. Shared résumé language, similar backgrounds, and changes in personal circumstances can have legitimate explanations.
B. Use AI to identify suspicious endpoint and network behavior
Security teams can apply machine learning to endpoint, identity, cloud, and network telemetry to identify patterns associated with unauthorized remote access or data theft.
Useful detection scenarios include:
- Remote-control software appearing on devices where it is not authorized.
- Unusual login patterns involving multiple locations, devices, or sessions.
- Unexpected access to source-code repositories, customer databases, or sensitive document stores.
- Unusual data-transfer volumes or repeated transfers to unapproved destinations.
- Software installations or system configurations inconsistent with an employee’s assigned role.
AI can correlate weak signals that individually appear unremarkable. For instance, a remote login might be legitimate, and a software installation might be harmless. A combination of unexplained remote access, a new external control device, and unusual outbound data transfers warrants closer examination.
The goal is to detect the pattern without assuming that any single event proves misconduct.
C. Improve incident response with AI assistants
Organizations can use approved AI tools to help analysts:
- Summarize security alerts and organize event timelines.
- Correlate relevant endpoint, identity, and network logs.
- Explain unfamiliar processes or software behavior.
- Draft investigation checklists and incident reports.
- Identify gaps in evidence collection and recommend next investigative steps.
- Develop defensive detection rules and test them against known scenarios.
AI-generated conclusions should be validated against the original logs and other evidence. Sensitive employee records, credentials, source code, and incident data should not be submitted to public AI services unless their use is explicitly authorized and appropriately protected.
D. Test defenses before an incident occurs
AI can help organizations conduct controlled exercises involving simulated identity fraud, impersonation, unauthorized access, and suspicious data transfers.
Security teams can use these exercises to test whether:
- Recruiters recognize identity-verification gaps.
- Endpoint controls block prohibited remote-access software.
- Security monitoring detects anomalous behavior.
- Incident responders preserve evidence and contain compromised accounts.
- Third-party contractors follow required security procedures.
These exercises should take place in authorized test environments and be measured against documented objectives.
E. Use AI carefully and account for false positives
AI detection is not a substitute for evidence. Deepfake detectors can misclassify legitimate video, behavioral systems can flag unusual but authorized activity, and automated systems may perform differently across populations or technical environments.
Organizations should measure false-positive and false-negative rates, document the basis for consequential decisions, restrict access to sensitive monitoring data, and provide a human review process.
The National Institute of Standards and Technology’s AI Risk Management Framework and its Generative AI Profile provide useful foundations for evaluating these risks.
5. AI as an attack tool: Why traditional hiring controls are no longer sufficient
The same capabilities that make AI useful to defenders can help fraudulent applicants scale and refine their activities. The FBI’s earlier guidance on North Korean IT worker schemes specifically identified the use of AI and face-swapping technology in video interviews, as well as assistance purchasing AI services. The October 2026 advisory describes a broader ecosystem of facilitators and identity misuse.
A. More convincing applications and professional identities
Generative AI can help produce polished résumés, cover letters, portfolios, technical explanations, and professional correspondence. It can also help a malicious actor maintain multiple seemingly distinct professional identities.
As a result, writing quality and a plausible technical portfolio are weaker evidence of identity than they once were.
Defensive response: Independently verify credentials, contact previous employers through trusted channels, validate claimed project contributions, and assess practical skills through work completed under controlled conditions.
B. Synthetic faces, voice cloning, and interview impersonation
AI-generated media can make it easier to impersonate another person during a video interview or meeting. Voice cloning and real-time audiovisual manipulation can further undermine confidence in what a recruiter sees and hears.
However, not every awkward video, audio delay, accent, or inconsistent background indicates fraud. Legitimate technical limitations and accessibility needs can produce similar observations.
Defensive response: Combine live interviews with independent identity checks, role-specific questions, follow-up sessions, and verification that the same person performs the work after hiring. For sensitive positions, use additional proportionate verification rather than relying on a single video call or a deepfake detector.
C. Automated preparation and third-party interview assistance
AI tools can help applicants rehearse answers, explain technical concepts, and generate plausible responses to questions. Human intermediaries can also conduct interviews or complete work on behalf of the person named in the application.
This makes it difficult to establish identity and capability through a conventional interview alone.
Defensive response: Use structured interviews, ask candidates to explain decisions made during practical exercises, and conduct follow-up discussions about their own work. Verify that the person hired is the person actually completing the assignment.
D. Scaling the recruitment operation
AI can reduce the time required to prepare applications and manage routine communications. Combined with human facilitators and subcontractors, this can allow a fraudulent operation to pursue many opportunities simultaneously.
Defensive response: Use cross-application analytics to identify patterns, establish consistent verification standards, and share relevant signals across HR, security, and compliance teams. Avoid relying exclusively on static lists of names or known indicators, which can quickly become outdated.
E. Improving the appearance of legitimacy
AI can help produce convincing business communications, supporting documents, and professional-looking websites. A fraudulent applicant or intermediary may therefore appear credible during initial screening.
Defensive response: Verify important claims through independent sources. Do not treat polished documentation, a convincing online presence, or an apparently authentic video as sufficient proof of identity.
The broader lesson is that AI can reduce the cost of deception while increasing the volume and plausibility of fraudulent activity. Defensive processes must therefore rely on evidence that is independently verified, rather than on how convincing an applicant appears.
6. A practical 30-day action plan for organizations
The following plan translates the advisory into a manageable set of initial priorities.
| Timeline | Priority actions | Intended outcome |
|---|---|---|
| Days 1–7 | Review remote hiring, identity verification, device shipping, contractor onboarding, and remote-access policies. | Identify immediate control gaps. |
| Days 8–14 | Verify privileged and sensitive remote accounts; audit remote-access software, external control devices, and administrative permissions. | Reduce unauthorized access opportunities. |
| Days 15–21 | Correlate HR, endpoint, identity, and network signals; test alerts for unusual remote access and data transfers. | Improve detection and investigation. |
| Days 22–30 | Exercise an insider-threat scenario, review third-party staffing controls, and document incident escalation procedures. | Validate readiness and assign remediation owners. |
After the initial month, organizations should establish recurring access reviews, periodic vendor assessments, detection testing, and continuous improvement based on investigation outcomes.
The plan should be adapted to the organization’s size, risk exposure, legal obligations, and available security resources.
7. What not to do: Avoid ineffective or unfair countermeasures
The FBI specifically warns that no single indicator can reliably identify these workers and that aggressive detection can generate false positives and harm legitimate employees.
Organizations should therefore avoid:
- Rejecting applicants solely because of their nationality, ethnicity, accent, or geographic background.
- Treating AI-detection scores as conclusive evidence.
- Assuming that every use of remote desktop software is malicious.
- Relying exclusively on static blocklists or name matching.
- Granting broad system access simply because an employee passed background checks.
- Collecting excessive personal data without a legitimate, documented purpose.
- Allowing an AI system to terminate employment or accuse an individual of misconduct without meaningful review.
Focus on verified identity, authorization, device integrity, actual behavior, and corroborated evidence. Apply consistent standards to comparable roles and provide a process for resolving mistaken flags.
Conclusion
The October 13, 2026, IC3 advisory illustrates how employment fraud can become an insider-security problem. The threat is not limited to an applicant submitting false documents. It can involve stolen identities, U.S.-based intermediaries, laptop farms, undisclosed subcontracting, unauthorized remote access, data exfiltration, and extortion.
AI increases the stakes on both sides. It can help defenders correlate signals, prioritize investigations, analyze security telemetry, and improve incident response. It can also help attackers produce convincing applications, impersonate people, prepare for interviews, and scale their operations.
The appropriate response is neither to rely on AI alone nor to abandon remote hiring. It is to build a layered system in which identity is verified independently, access is limited, devices are managed, behavior is monitored, third parties are accountable, and suspicious activity is investigated fairly.
The most important principle is simple: verify identity before granting trust, continue validating that trust throughout employment, and never confuse a convincing digital presence with proof of a legitimate person and a legitimate working arrangement.
Sources and further reading
- FBI IC3, North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment — October 13, 2026 .
- U.S. Department of Justice, Coordinated actions to combat North Korean remote IT worker schemes — October 13, 2026 .
- FBI, North Korean IT Workers Conducting Data Extortion .
- NIST, Artificial Intelligence Risk Management Framework .