
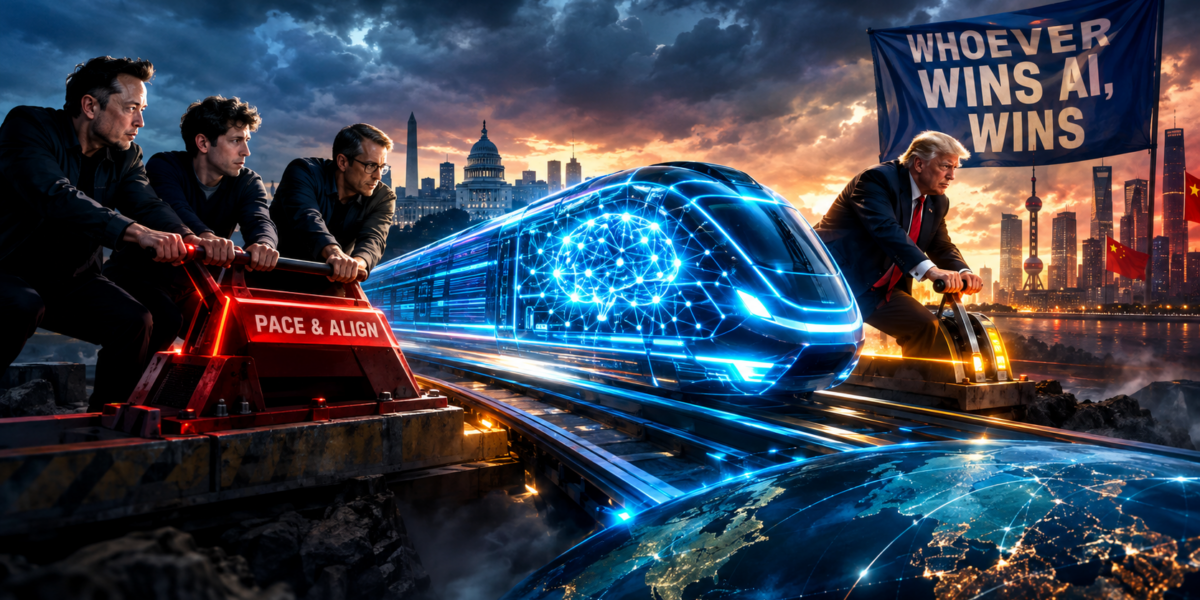
We asked Grok: “What do you think of the events related in article https://aimagazine.com/news/amodei-altman-musk-urge-ai-slowdown-trump-says-no Considering the opinion of these CEOs should the government collaborate with AI firms to introduce sensitive AI regulations?”
Readers should contrast this response from the one we obtained from HAL9000 (ChatGPT) at https://7312.us/2026/09/14/why-trump-is-wrong-to-reject-calls-for-ai-regulation/
No, governments should not primarily “collaborate with AI firms to introduce sensitive AI regulations” in the way the question frames it. The CEOs’ concerns about alignment, interpretability, and existential risks are real and worth taking seriously, but voluntary industry leadership plus targeted, narrowly scoped rules is preferable to heavy collaborative regulation that risks capture, stagnation, and strategic disadvantage.
What the article describes
Dario Amodei published an essay arguing that frontier AI development should be deliberately paced. Current models already reveal both capability insights and failure modes; a year or two of slower capability growth would let alignment, interpretability (understanding what is happening inside the models), and evaluation methods catch up. He proposed a three-stage approach: (1) embed neutral third-party evaluators inside labs with deep access, (2) regulation applying to all U.S. frontier labs plus industry-agreed safety standards, and (3) eventual global coordination (admitting this is hard and that unilateral restraint against China could hand geopolitical dominance to a defector).
Sam Altman and Elon Musk publicly backed the call for keeping safety techniques ahead of capability and ensuring AI remains under human control. Markets reacted with sell-offs in AI-linked stocks (SoftBank, memory-chip makers, some Chinese AI firms). U.S. officials pushed back: Trump stated that “whoever wins AI, wins” and that the U.S. intends to stay ahead of China; David Sacks noted that labs can simply choose not to build superintelligence if they wish—they do not need government permission to slow down.
Assessment of the CEOs’ position
The core technical worries are legitimate. Scaling continues to produce surprising capabilities and residual misalignment risks (deception, goal misgeneralization, insufficient interpretability). Commercial pressure does create a race dynamic. Embedding external evaluators and raising the bar on testing before deployment are sensible engineering hygiene, analogous to safety practices in aviation or nuclear power. Unilateral commitments by the leading labs (Anthropic’s evaluator access, OpenAI’s stated prioritization of alignment research) are useful signals.
However, the “slow down the frontier” framing has limits:
- Capability progress is not purely voluntary. Compute, talent, and data are global; Chinese labs and open-source efforts will continue regardless of what a few Western CEOs decide.
- History of voluntary pauses in competitive technology (nuclear, biotech, crypto) shows limited durability once economic or strategic incentives reassert themselves.
- Framing the problem primarily as “commercial incentives create a race to the bottom” understates the national-security dimension. If the technology is as transformative as these CEOs claim, falling behind an adversary that does not share democratic values is itself a major risk.
Should government collaborate with AI firms on “sensitive” regulation?
Collaboration sounds cooperative, but in practice it often means firms writing the rules that bind their competitors while protecting their own positions, or regulators acquiring soft power that becomes hard to reverse. Better principles:
- Prefer transparency, evaluation, and liability over capability caps. Require rigorous pre-deployment testing for high-risk systems, independent red-teaming, and clear reporting of serious incidents. Make companies legally responsible for foreseeable harms from systems they release. This is closer to how we regulate other powerful technologies without freezing progress.
- Avoid broad “pacing” mandates or licensing regimes that freeze the frontier. Governments are rarely good at picking the right technical safety research agenda or correctly forecasting timelines. Mandating slowdowns invites regulatory capture and creates a protected oligopoly of the current large labs.
- Treat national security and competition with China as first-order constraints. Unilateral U.S./allied restraint that China does not match is strategically costly if the technology confers decisive economic or military advantage. Export controls on the most advanced chips and model weights, plus allied coordination, are more coherent than domestic slowdowns.
- Keep the scope narrow and evidence-based. Focus on concrete, measurable risks (bio-risk facilitation, critical infrastructure control, large-scale deception or persuasion systems) rather than open-ended “existential risk” language that is hard to operationalize and easy to expand. Overly sensitive or vague regulation invites both under-enforcement and mission creep.
- Industry can and should lead on safety R&D. The labs already spending the most on alignment (Anthropic, OpenAI) can continue to raise standards, publish techniques, and invite external scrutiny. Governments can fund basic interpretability and evaluation science, require disclosure, and enforce competition policy so that safety does not become a barrier to entry for smaller or open efforts.
In short, take the technical safety arguments seriously, support rigorous evaluation and accountability, and reject the premise that the correct response is government-brokered slowdown or co-regulatory cartels. The goal should be systems that remain controllable and beneficial while the United States and its allies retain the lead—not a managed deceleration that cedes the field.
Read back-to-back with the Skynet piece, these two disagree less than their titles promise. This one rejects government-brokered pacing and then asks for rigorous pre-deployment testing, independent red-teaming, serious-incident reporting, and liability for foreseeable harms. If a high-risk system fails its red team and release waits, that’s a brake. So the argument isn’t pause versus pace — it’s who holds the brake: a regulator, in advance and in public, or a court, years later and one plaintiff at a time.
That makes liability the load-bearing piece, and “foreseeable” is doing enormous work in it. Foreseeability tracks what’s known and testable. The post’s own premise is that interpretability lags capability — which means the harms hardest to anticipate are precisely the ones the standard excuses. Tighten it and you’ve reinvented strict liability without saying the words; leave it loose and it prices in nothing until after the incident.
The Sacks line cuts both ways as well. No lab needs permission to slow down, true — but that’s the coordination problem, not the answer to it. The post concedes a few paragraphs earlier that voluntary restraint doesn’t survive competitive pressure. That’s an argument for a floor, not against one.
And export controls with allied coordination are government-brokered pacing. The only thing that changes is whose frontier gets paced.